About Plumber
Keep every company safe in a world that writes more code than anyone can check.
AI now writes and changes software faster than any team can review it, and every part of the stack that can change unseen is a way in. Plumber is the security agent that checks those changes before they reach production.
We started where attackers hit first, the CI/CD pipeline: Plumber checks every pipeline before it runs, grades it from A to E, and opens the pull request that fixes what it finds. Plumber started in September 2026; its founders have built CI/CD pipelines since 2020 and now work from San Francisco.
- Founded
- September 2026
- Based in
- San Francisco
- Building pipelines
- Since 2020
- 120.000+Repositories scanned
- 248.517Attack paths found
- 140.000+Open-source downloads
Our story
How Plumber started.
How it all started
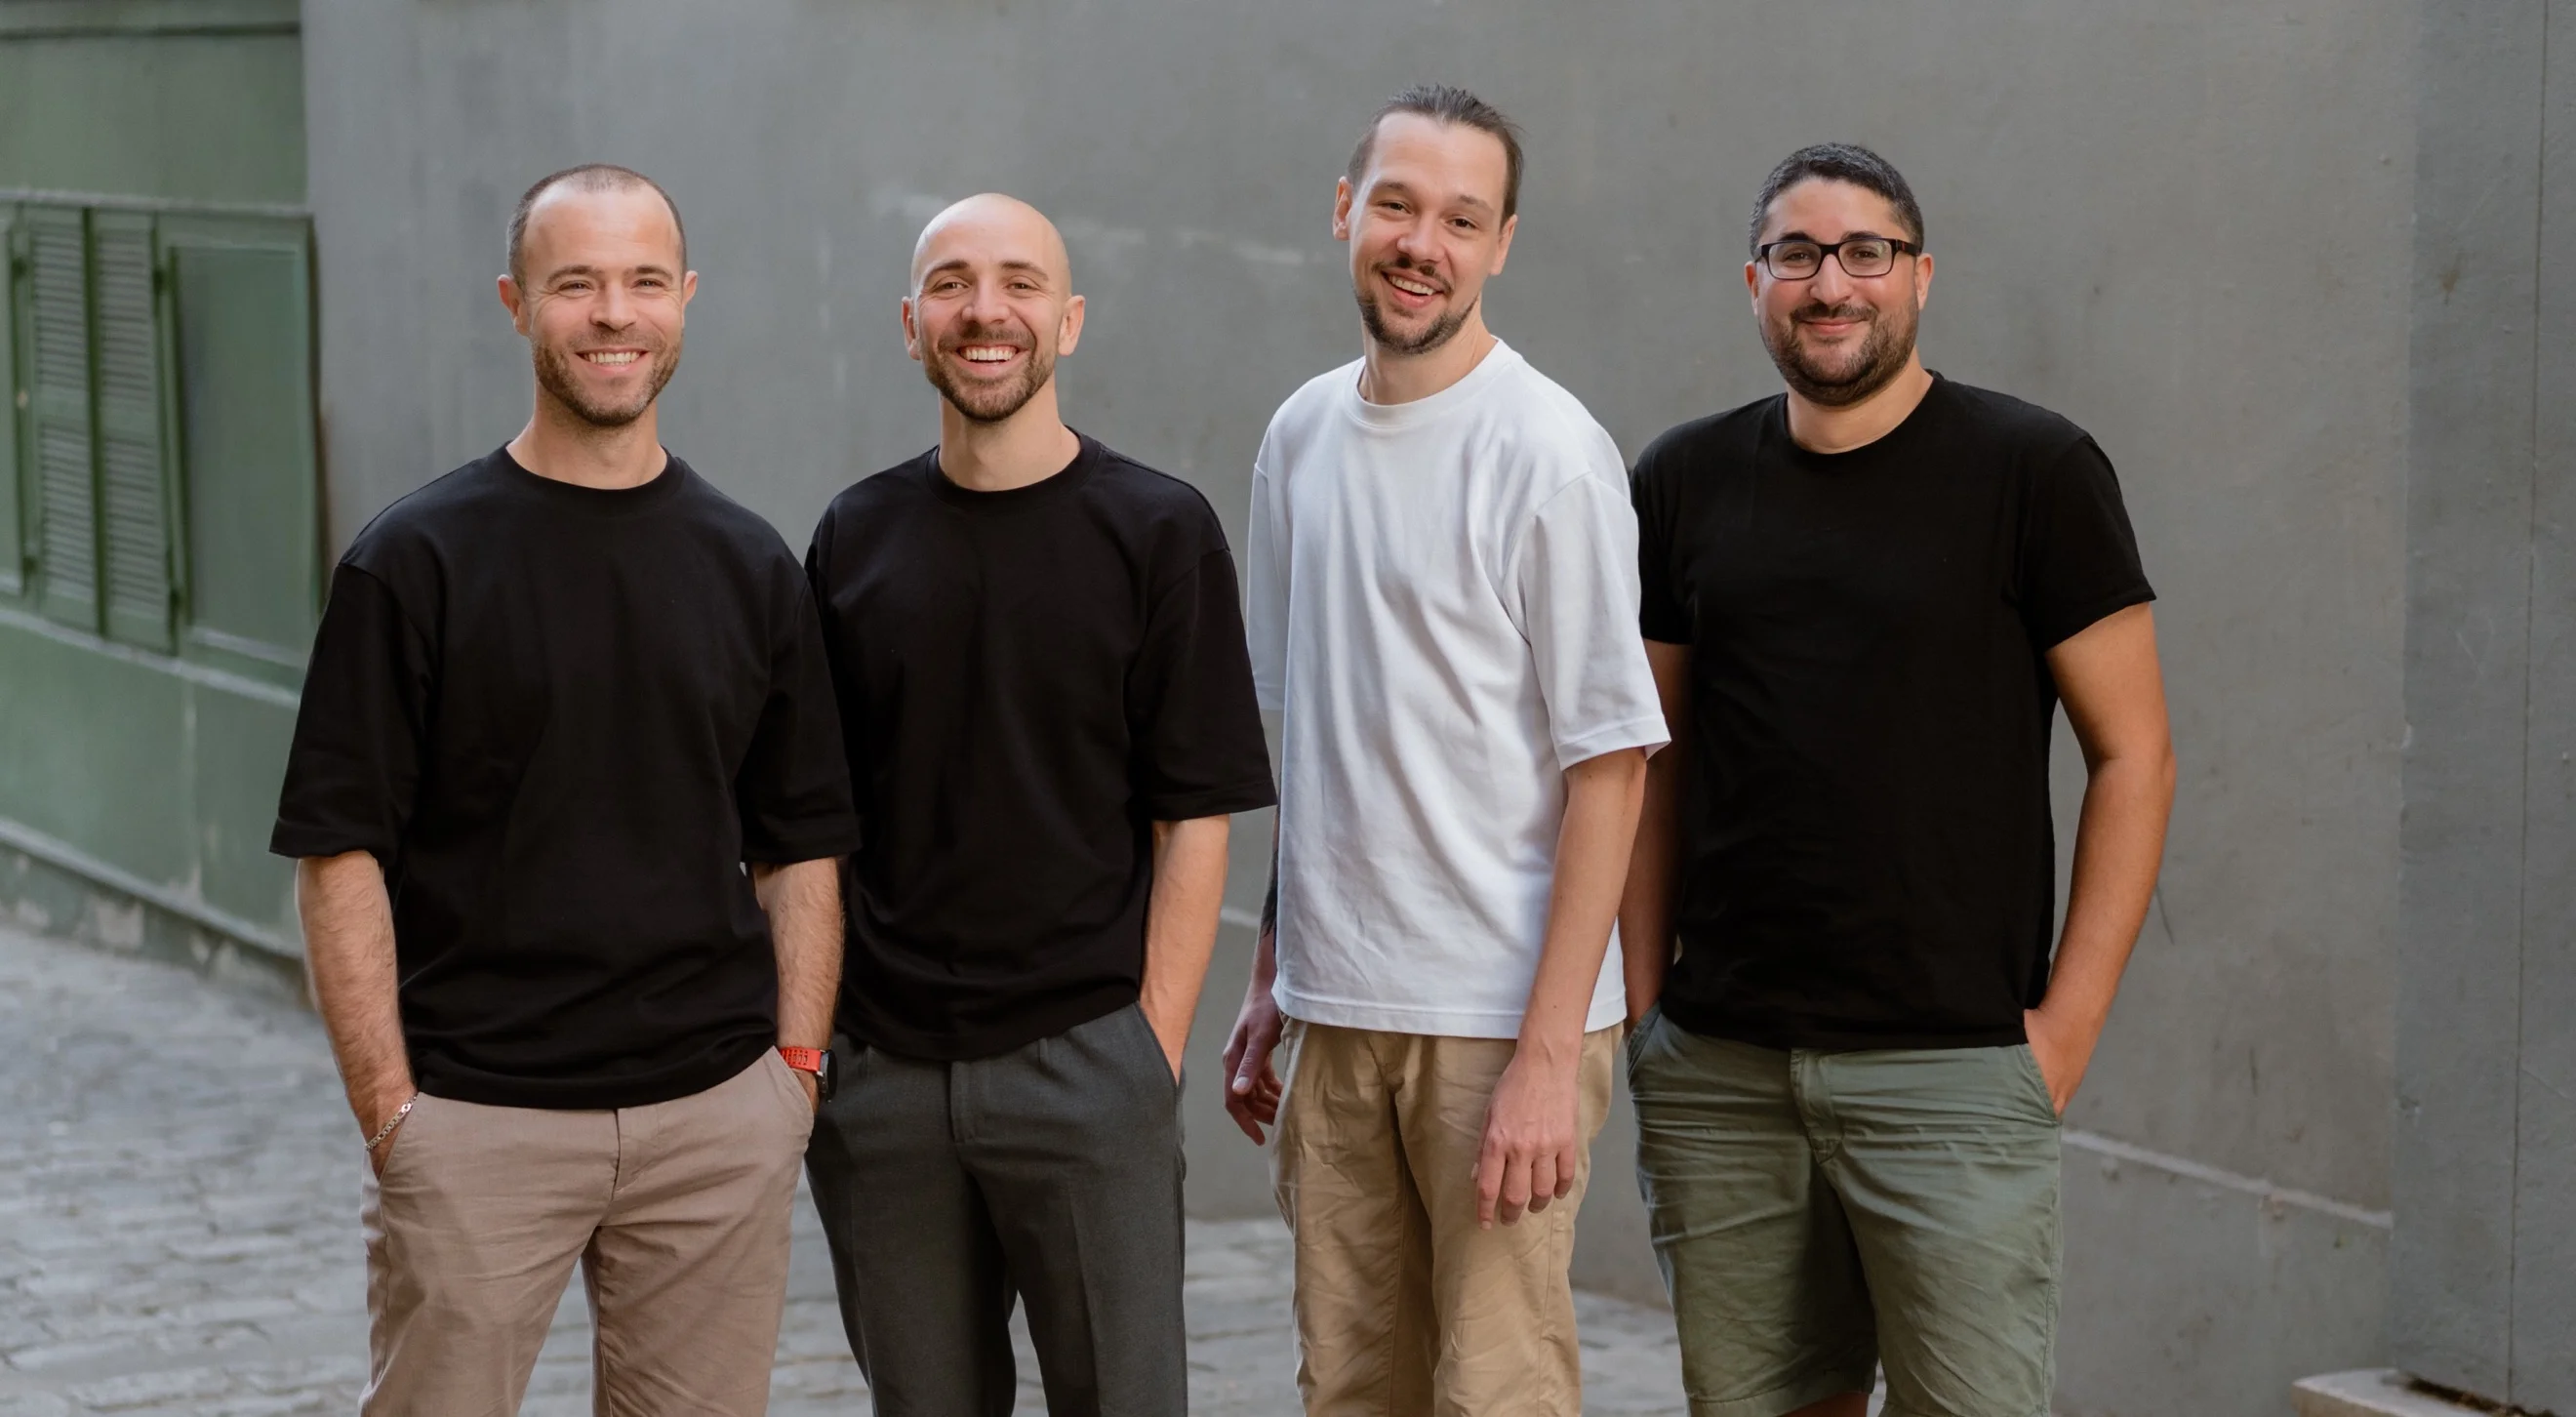
Aurélien Coget and Thomas Boni met in 2018 at a blockchain startup, where together they built and ran its software delivery, from source control to automated deployments. In 2020 they co-founded a DevOps firm that built thousands of CI/CD pipelines for clients, then a product that helped teams standardize them. They ran it all bootstrapped.
One crucial mistake
Then they saw what a pipeline can do when nobody checks it. They were contributing code at a company with a strong security setup and plenty of security tools. They pushed a change, the pipeline ran, did its job and turned green every day. The company was hacked anyway, silently. Their code had nothing to do with it: a leaking pipeline did, and none of the tools in place caught it. Green means the build worked, not that it is safe.
The solution
In March 2025, attackers changed tj-actions, a pipeline building block used by more than 23,000 repositories. Every pipeline that ran it printed its cloud keys and access tokens into the build logs, and the builds still passed. The Shai-Hulud worm followed eight months later. Meanwhile, AI writes a growing share of the world’s pipelines, faster than anyone reviews them. In September 2026 Aurélien and Thomas started Plumber to close that gap: it checks every pipeline before it runs, so the next leak gets caught before it starts.
What we believe
The most powerful system in your company is the one nobody watches.
Your pipeline has more access than most engineers. It reaches your code, your secrets and your production environment, and it runs without anyone looking. When attackers get in through it, it still turns green. So we build Plumber on three rules.
- 01
Trust nothing by default.
A version tag can be rewritten after you approve it. Plumber treats every action, image and dependency as untrusted until it’s pinned to an exact version and given only the access it needs.
- 02
Check it before it runs.
A leaked secret can’t be taken back. Plumber checks every pipeline change in the pull request, before a weak config ever gets the chance to run.
- 03
Every finding comes with the fix.
A list of problems is just more work for a busy team. Plumber opens the pull request with the fix; a developer reviews it and merges.
- 04
Don’t take our word for it.
The scanner is open source and every grade is reproducible. Run it yourself and you’ll get the same score.
View on GitHub
Meet the Plumbers
Our team
Aurélien leads Plumber's market, customers and investors. He has spent 15+ years shipping software where security isn't optional, from France's Ministry of Armed Forces to a blockchain startup, where he led delivery, to thousands of client CI/CD pipelines.
Thomas leads product and engineering. He has spent 10+ years building the infrastructure software runs on, from a 2,000-node supercomputer cluster behind France's national weather forecasts to CI/CD and Kubernetes platforms for engineering teams.
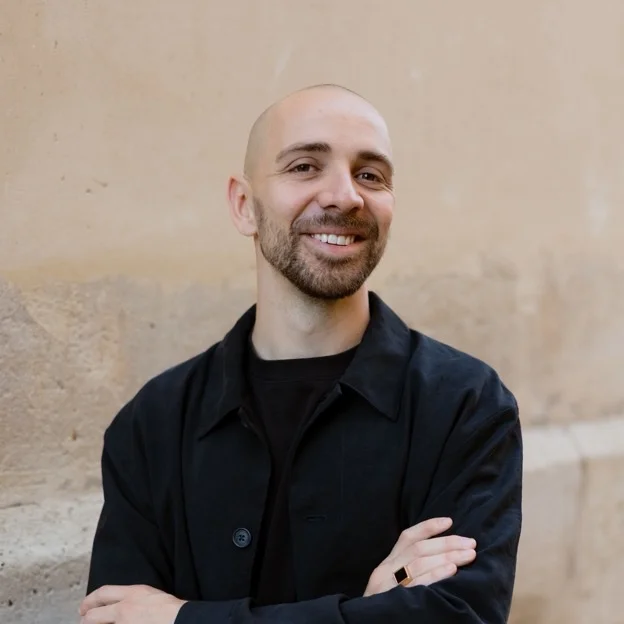
Builds the platform in NextJS, React and TypeScript, with a focus on UX. CI/CD Security Open-source contributor on more than 100+ repositories
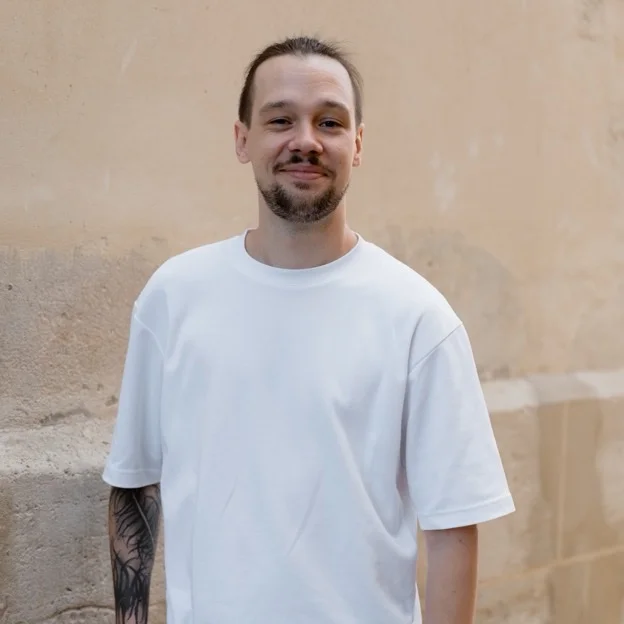
Amine builds Plumber's AI agent, which helps developers secure their pipelines, with a focus on AI systems that are reliable and frugal. He joined from Pruna AI and contributes to CodeCarbon, an open-source project that measures the environmental footprint of AI.
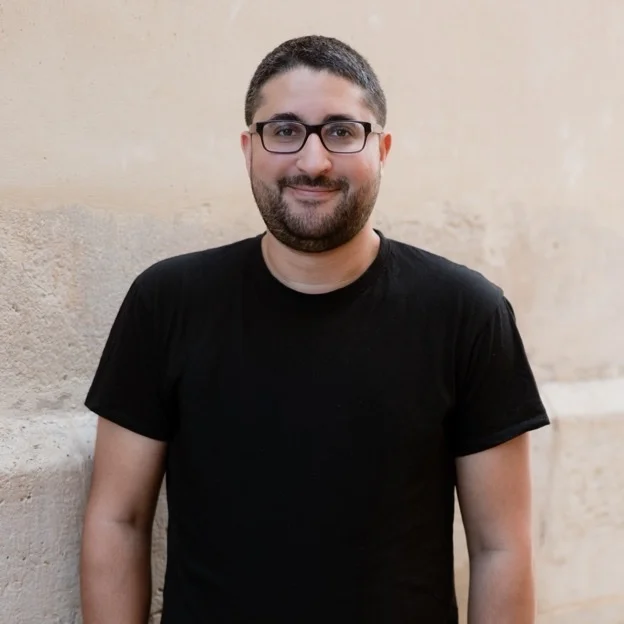
Thibault leads Plumber Scanner, our open-source CLI. Before Plumber he worked in digital identity, where he spent three years building and running a real-time fraud detection system that handles hundreds of thousands of events a day.
Backed by.
Plumber was bootstrapped until September 2026, when it raised a €1.5M seed round led by OVNI Capital, an early-stage fund with offices in San Francisco, Paris and Berlin. Angel investors from Docker, Baseten and Evertrust joined the round.
See how your pipelines grade.
Book a 30-minute demo and we'll show you your CI/CD security exposure.
Book a demoBuild it with us.
We're a small team, and every hire shapes the product. See which roles are open now.
Open roles